Posts

Showing posts with the label av

Symantec Endpoint Protection...again

Wow. I've really had LOTS of hits generated on this blog, since I posted some info about SEPM and my related issues, so I've decided to share some tips and other interesting findings. My guess is that many of you that hit my blog don't have the luxury of having a DEV environment to test in, so PLEASE do yourself a favor, and if you do nothing else, follow #7 and #8. This will prevent you from having to invest in the Hair Club for Men after you yank all yours out. Tips: SEPM doesn't like to be installed on custom HTTP ports, but it is possible. See 'Configuring the Symantec Endpoint Protection Manager to run with a custom HTTP port' Document ID: 2007111212591048 here . It's a pretty simple process. SEPM will not show graphics from RDP sessions....seriously. So don't put yourself in a situation as I did, and hang on the helpline-from-hell with someone that didn't know, nor did the knowledge-base. DOH! If you have to upgrade SEPM, God help you. I used...
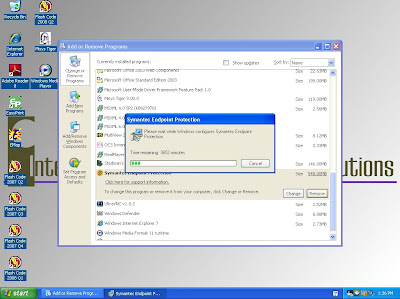
2.5 Days to uninstall Symantec Endpoint Protection client

Image
So today I'm trying to clean up a Symantec Endpoint Protection client install that went bad, and here's what I get during the uninstall process... Is it really gonna take this long? Can I make a pot of coffee stretch that far? Will my kids start college before this completes? In truth, this quickly went to 11 M$ minutes, then to 1 M$ minute. First time I've EVER seen anything like that before.

Symantec Endpoint Protection...blech

My SEPM server decided to do the BSOD the other night, at about 2:00am. Nice. Right when a few users from India were working on the server, which also happens to be our Terminal Server. Thankfully, I didn't get a call. I can't wait until MR2 comes out. Some of the touted improvements is a lighter weight processor footprint, fixed graphics (mine ALWAYS work at the console, just not remotely...), and I'm sure numerous other fixes. I hope I don't have to run around the office yet AGAIN to use their sylink tool reconnect my clients. I had originally scripted it, but it doesn't work if you impose password protection on the UI...hmph... I'd also found that logging on some of the clients was out of control. Saw many posts on Symantec's user forums to this affect, and my uninstalling and reinstalling seemed to fix that, for now.

Symantec Endpoint Protection...is a PIG

I just spent the last few days troubleshooting a Symantec Endpoint Protection migration from Symantec Antivirus Corporate Edition v10.x. What an effort. Much like the last time I upgraded a client from 9 to 10. They conviently forgot to include "May bring your older, underpowered workstations to their KNEES." in the product description. That client had about 25 workstations that were old HP workstations, runnning Windows 2000 on 256kb RAM and 500mHz CPU's. Once they started up, the "Startup Scan" would bring the machine to a crawl, and only perform well when it completed, which for those old things was quite a while. Nice of them to release a registry hack to disable that...then they release a config option in the next patch...NICE. Also forced the client to bump all the workstations RAM to 512. Nice for my billable hours, but not for their non-profit wallet. This time the environment is much different, and I "own" it. That is to say, I'm back to...